
Developer portal
Qtangl PQC scanner
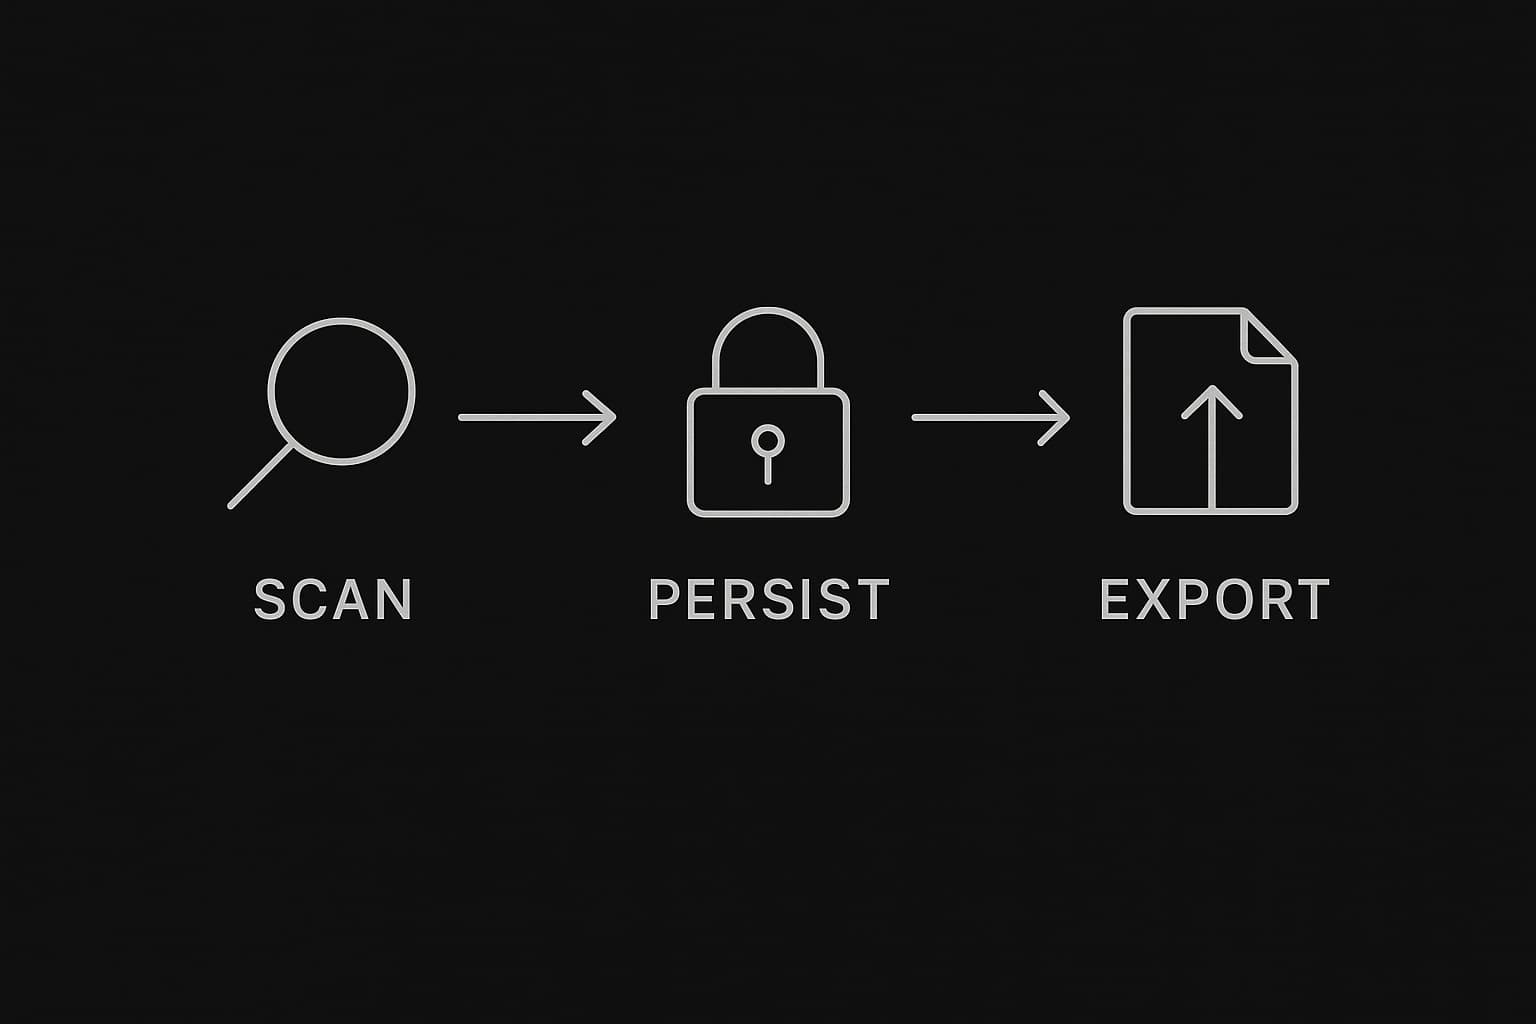
Scan domains for quantum-vulnerable crypto, export CycloneDX CBOM, and generate signed reports with verify links.
Last updated: 2026-06-21
Post-quantum readiness
Live TLS inventory, Mosca HNDL scoring, CBOM exports, and signed PDF evidence — Assess → Monitor → Convert.
When to use the PQC scanner
- Board or regulator mandate to inventory quantum-vulnerable cryptography.
- CMMC, PCI-DSS 4.0, or HIPAA audit needs crypto control evidence.
- You need continuous drift monitoring — not a one-time spreadsheet.
Inventory aid, not formal audit. Signed evidence your GRC team can verify.
Start here — PQC journey
PQC guides & reference
PQC demo guide
Live scan workflow, scenarios, CBOM export, and verify links.
PQC API reference
Scan, inventory, report, and standards endpoints.
Standards mapping
NSM-10, CNSA 2.0, NIST IR 8547, and framework crosswalk.
Q-Day hub
HNDL, Mosca inequality, deadlines, and CBOM education.
Documentation map
Core Workflow
Verify & Trust
PQC API reference
- API guide
- GET /pqc/inventory
- GET /pqc/scenarios
- GET /pqc/target
- GET /pqc/handshake-trace
- GET /pqc/standards
- POST /pqc/upload-bundle
- POST /pqc/scan
- GET /pqc/scan/{scanId}
- POST /pqc/handshake/prove
- GET /pqc/report/{scanId}
- POST /pqc/cbom/ingest
- POST /pqc/scan/{scan_id}/persist
- GET /pqc/report/{scan_id}/availability
- GET /pqc/verify/{scan_id}
- POST /pqc/verify
- GET /pqc/index
- GET /pqc/index/drift
- GET /pqc/transparency/consistency
- GET /pqc/transparency/witnesses
- POST /pqc/transparency/witness
- GET /pqc/transparency/root
- GET /pqc/transparency/keys
- GET /pqc/transparency/{content_hash}
- POST /pqc/transparency/keys/retire
- GET /pqc/cbom/sources
- GET /pqc/cbom/aggregate
- GET /pqc/cbom/conflicts
- PUT /pqc/cbom/conflicts/{conflict_id}
- GET /pqc/cbom/diff
- POST /pqc/cbom/pull/{provider}
- POST /pqc/scan/{scan_id}/remediation/simulate
Tenant API — Scans & reports
- RBAC & scopes
- GET /tenant/passports
- GET /tenant/scans
- GET /tenant/scans/{scan_id}
- DELETE /tenant/scans/{scan_id}
- POST /tenant/scans/{scan_id}/email
- GET /tenant/scans/{scan_id}/remediation
- POST /tenant/scans/{scan_id}/remediation
- POST /tenant/scans/{scan_id}/remediation/automate
- GET /tenant/scans/{scan_id}/remediation/intelligence
- POST /tenant/scans/{scan_id}/remediation/simulate
- POST /tenant/scans/{scan_id}/remediation/verify
- GET /tenant/scans/{scan_id}/report
- POST /tenant/scans/{scan_id}/share
- DELETE /tenant/share/{link_id}
Tenant API — Monitor & ops
- PATCH /tenant/alerts/{alert_id}/read
- POST /tenant/alerts/read-all
- GET /tenant/analytics/anomaly
- GET /tenant/analytics/forecast
- GET /tenant/analytics/readiness-trend
- POST /tenant/analytics/track
- GET /tenant/audit
- GET /tenant/audit/export
- GET /tenant/benchmarks
- POST /tenant/dashboard/digest/preview
- POST /tenant/dashboard/digest/send-test
- GET /tenant/dashboard/events
- GET /tenant/dashboard/recommendations
- GET /tenant/dashboard/summary
- GET /tenant/dashboard/tab/{tab_name}
- GET /tenant/drift-intel
- GET /tenant/evidence
- POST /tenant/evidence/{scan_id}/retain
- GET /tenant/export
- POST /tenant/recommendations/{recommendation_id}/dismiss
- POST /tenant/scans/batch
- POST /tenant/scans/bulk-export
- GET /tenant/schedules
- POST /tenant/schedules
- PATCH /tenant/schedules/{schedule_id}
- DELETE /tenant/schedules/{schedule_id}
- GET /tenant/schedules/{schedule_id}/runs
- POST /tenant/schedules/batch
- GET /tenant/slo
- GET /tenant/webhooks
- POST /tenant/webhooks
- DELETE /tenant/webhooks/{webhook_id}
- GET /tenant/webhooks/dlq
- POST /tenant/webhooks/replay
Tenant API — Integrations
- POST /tenant/cloud-import
- GET /tenant/coverage/cloud/{provider}
- POST /tenant/coverage/code-scan
- GET /tenant/integrations
- POST /tenant/integrations/{provider}
- POST /tenant/integrations/clm/{clm_provider}
- POST /tenant/integrations/clm/{clm_provider}/test
- GET /tenant/integrations/cloud
- POST /tenant/integrations/cloud/{provider}
- POST /tenant/integrations/cloud/{provider}/test
- POST /tenant/integrations/keyfactor
- POST /tenant/integrations/keyfactor/test
- POST /tenant/integrations/pull
- POST /tenant/scans/{scan_id}/integrations/push
Tenant API — Admin & team
- POST /tenant/ai/explain
- POST /tenant/ai/explain-portfolio
- POST /tenant/ai/explain-scan
- GET /tenant/api-keys
- POST /tenant/api-keys
- DELETE /tenant/api-keys/{key_id}
- GET /tenant/authorized-domains
- POST /tenant/authorized-domains
- PATCH /tenant/authorized-domains
- POST /tenant/billing/checkout
- POST /tenant/billing/portal
- GET /tenant/billing/portal
- GET /tenant/compliance/posture
- DELETE /tenant/data
- GET /tenant/invites
- POST /tenant/invites
- DELETE /tenant/invites/{invite_id}
- POST /tenant/legal/accept
- GET /tenant/me
- GET /tenant/members
- PATCH /tenant/members/{membership_id}
- DELETE /tenant/members/{membership_id}
- POST /tenant/offboard
- GET /tenant/oidc
- PUT /tenant/oidc
- PATCH /tenant/onboarding
- GET /tenant/settings
- PUT /tenant/settings
- POST /tenant/sso/portal-link
- PATCH /tenant/workspace
Tenant API — Portfolio & MSSP
Discovery depth
Integrations
Admin & billing
- Admin & key lifecycle
- GET /admin/analytics/funnel
- DELETE /admin/keys/{key_id}
- GET /admin/platform/summary
- GET /admin/tenants
- POST /admin/tenants
- GET /admin/tenants/{tenant_id}
- PATCH /admin/tenants/{tenant_id}
- PUT /admin/tenants/{tenant_id}/authorized-domains
- POST /admin/tenants/{tenant_id}/keys
- GET /admin/tenants/{tenant_id}/keys
- PUT /admin/tenants/{tenant_id}/mssp-parent
- PUT /admin/tenants/{tenant_id}/settings
- GET /admin/users
- Billing & onboarding
- GET /demo/campaign/{campaign_id}/state
- GET /demo/compliance
- GET /demo/events
- GET /demo/graph
- GET /demo/narration
- GET /demo/portfolio
- GET /demo/scenes
- GET /demo/status
- GET /demo/trend
- GET /demo/verify/{snapshot_id}
- POST /public/assess-signup
- POST /public/lead-capture
- POST /public/monitor-provision
- POST /public/monitor-signup
- GET /public/onboarding-key/{token}
- POST /public/stripe-webhook
- POST /public/unsubscribe
- GET /public/verify/branding
- POST /public/workos/webhook
- GET /r/{token}
- GET /r/{token}/report
Operations
Trust & compliance
What it is
Assess → Monitor → Convert with signed evidence on every assessment.
Three tiers
- 1. Assess — baseline scan, Mosca HNDL, CBOM, signed PDF.
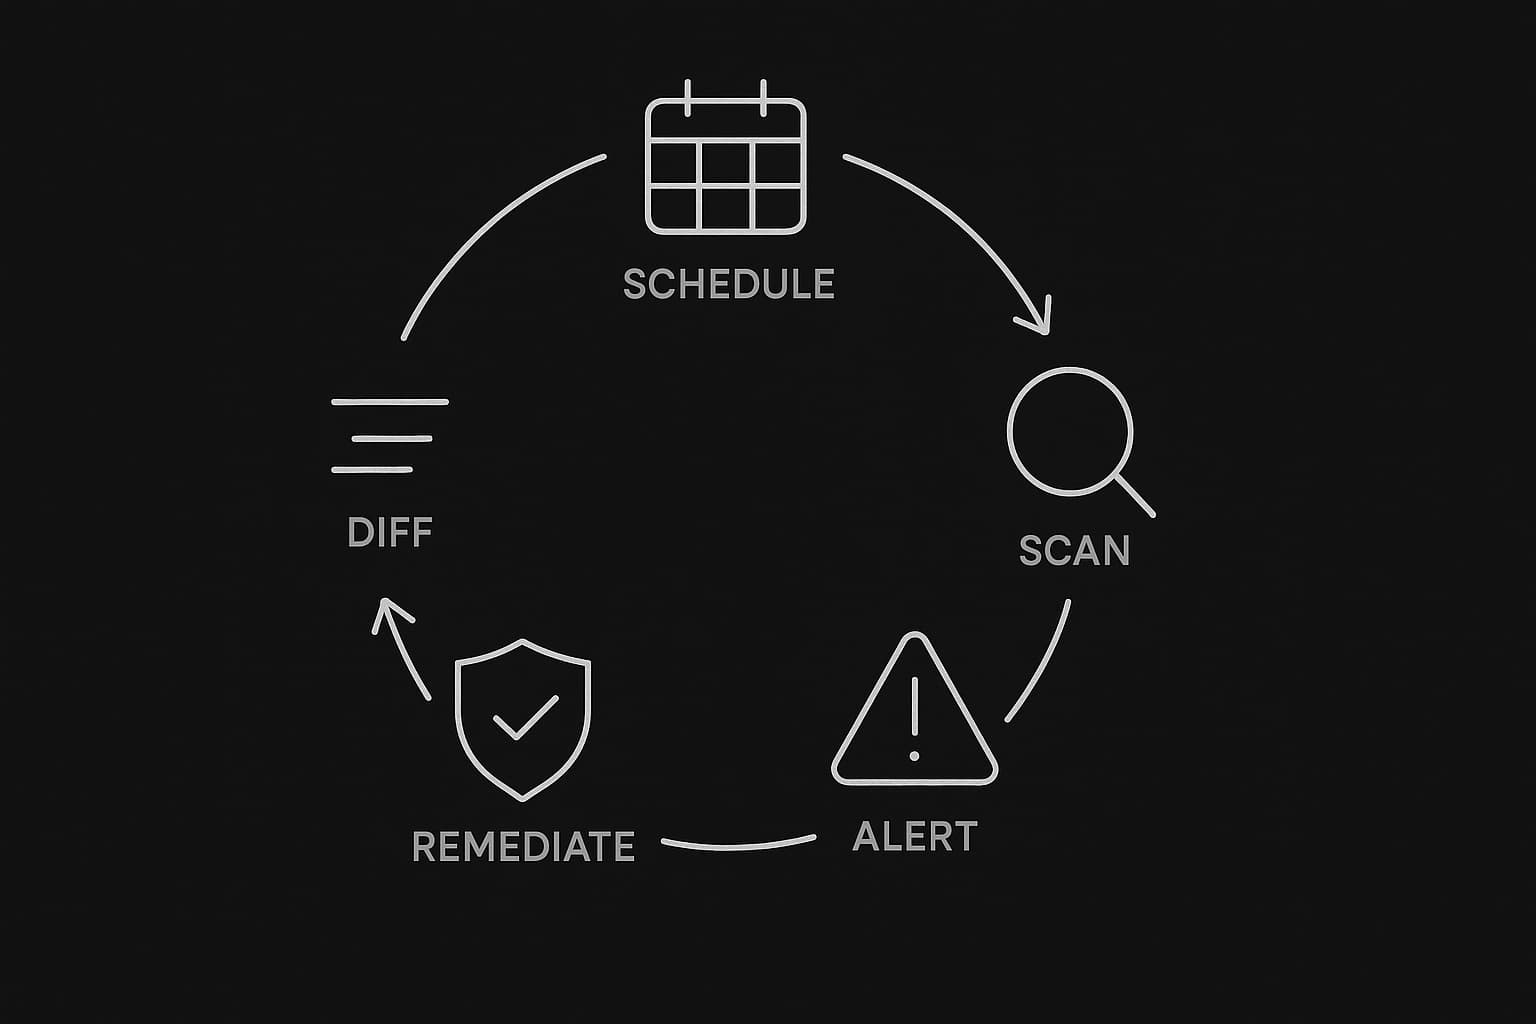
- 2. Monitor — scheduled re-scans, diff alerts, remediation board.
- 3. Convert — playbooks, workshops, re-scan verification.
Found an issue? Report documentation feedback