
Education
Where cryptography hides: an attack surface map for PQC migration
Teams that inventory only public HTTPS miss most of the long-tail crypto their auditors care about. This map shows where quantum-vulnerable algorithms hide.
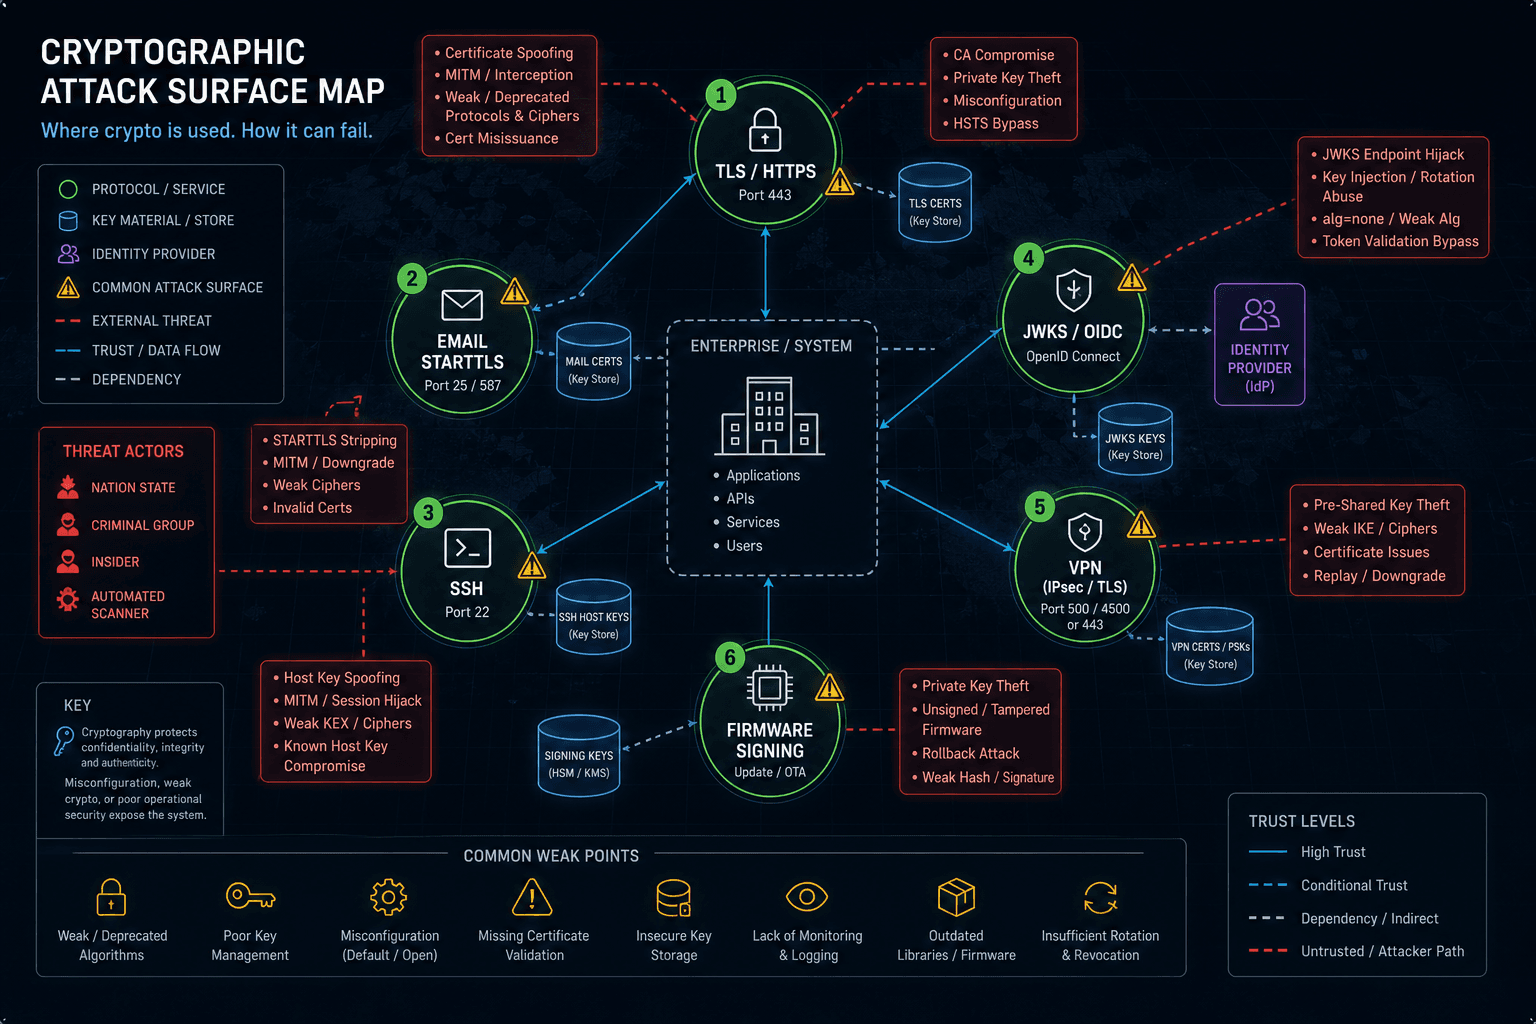
Attack surface layers
Internet-facing          Internal / partner           Embedded & supply chain
─────────────────        ─────────────────────        ─────────────────────────
HTTPS / API TLS          mTLS between services        Firmware signing (RSA)
CDN cert chains          LDAPS / database TLS         Secure boot keys
Email STARTTLS           VPN (IPsec, WireGuard)       IoT device certs
JWKS / OIDC keys         SSH host keys                Container image signatures
NIST IR 8547 expects organizations to discover crypto across the full estate. The NCCoE migration project publishes discovery guidance.
Common blind spots
- OAuth/OIDC JWKS endpoints serving ECDSA keys for token signing
- SMTP STARTTLS on notification and claims systems
- Backup encryption using RSA-wrapped symmetric keys
- Third-party SaaS where you control policy but not implementation
NIST's PQC overview and Palo Alto's Q-Day guide emphasize breadth over depth on a single domain.
Inventory approach
- External TLS baseline (fast, high signal).
- Expand to JWKS, SSH, and email from asset lists.
- Merge into CycloneDX CBOM with provenance tags.
- Re-scan on change cadence — see crypto drift blog.
This quarter
- Map your estate against the layers above; mark coverage gaps.
- Run external scan + manual JWKS/SSH checklist.
- Export CBOM and assign owners per finding category.
Continue on the Q-Day hub: CBOM guide
References & further reading
Authoritative primary sources cited in this article. Summaries are our own — follow links for full context.
Last verified 2026-06-21
- NIST IR 8547: Transition to Post-Quantum Cryptography StandardsNIST · 2024Federal transition guidance with deprecation timelines for quantum-vulnerable algorithms.
- What Is Post-Quantum Cryptography?NIST · 2024Official overview of NIST's PQC project, finalized standards, and the harvest-now-decrypt-later threat model.
- What Is Q-Day? Quantum Computing and Cyber RiskPalo Alto Networks · 2026CRQC definition, HNDL threat model, and migration guidance for enterprise security teams.
- NCCoE Migration to Post-Quantum Cryptography ProjectNIST NCCoE · 2024Practical migration demos, crypto discovery guidance, and industry collaboration.
- What Makes Quantum Computers SO Powerful?Veritasium (YouTube) · 2023Covers Shor's threat, harvest-now-decrypt-later, NIST PQC competition, and migration urgency.
See your exposure with evidence
Run a live PQC inventory scan, export a CBOM, and verify signed reports independently.